For most of its early life, the NIS2 Directive was discussed as a deadline. The main questions were when each country would turn it into national law and when organizations would formally fall under the rules. In 2026, those questions have largely been answered. The great majority of member states have transposed NIS2, national supervisory authorities are moving from writing rules to overseeing against them, and the European Commission has taken several late member states to the EU Court of Justice for missing the transposition deadline. NIS2 has moved from something organizations were preparing for into something they are now measured against.
That shift changes what "compliance" has to mean in practice. Having the right policies on file was a reasonable answer to a deadline. It is a weak answer to an auditor who wants proof that a control works, or to a 24-hour reporting clock that starts when the organization becomes aware of a significant incident. This article looks at where NIS2 enforcement stands today, what the directive actually requires, what certification does and does not mean under NIS2 (an area full of misunderstanding), and how cyber range testing helps organizations prove they are ready rather than simply claiming it.
What Is the NIS2 Directive?
NIS2 is the European Union's main cybersecurity law. It replaced the original 2016 NIS Directive with a broader, stricter regime, and its goal is to raise the level of cyber security across the EU for the sectors that society and the economy depend on, from energy, transport, water, and health to banking, digital infrastructure, public administration, and space.
In short, NIS2 does two things. It requires in-scope organizations to put a defined set of cybersecurity risk-management measures in place, and it requires them to report significant incidents to the authorities within strict deadlines. It also sorts organizations into two groups, "essential" and "important" entities, which face different levels of supervision and different penalties.
Who Does NIS2 Apply To?
NIS2 covers organizations in 18 sectors, split into two annexes. Annex I lists the "high-criticality" sectors: energy, transport, banking, financial market infrastructure, health, drinking water, waste water, digital infrastructure, ICT service management, public administration, and space. Annex II lists "other critical" sectors: postal and courier services, waste management, chemicals, food, certain manufacturing, digital providers such as online marketplaces and search engines, and research.
Two factors then decide whether you are in scope and which category you fall into: your sector and your size.
· Size threshold (a screening rule, not the whole test). As a rule, NIS2 applies to medium-sized and larger organizations: broadly, 50 or more staff, or annual turnover or a balance-sheet total above €10 million. The calculation follows the EU's SME definition, so linked and partner companies count towards the totals and can pull a smaller entity into scope. Small and micro organizations are generally out, but the figures are a first filter, not the final answer.
· Essential entities, as a general rule, are large organizations (250+ staff, or turnover above €50 million / balance sheet above €43 million) in an Annex I high-criticality sector. But size is not the only route in: several types of entity are essential regardless of size (see below), and even medium-sized providers of public electronic communications networks or services are treated as essential.
· Important entities are medium-sized organizations in Annex I sectors, and qualifying organizations in Annex II sectors.
· Regardless of size, some organizations are in scope, and several are classed as essential outright, including qualified trust service providers, top-level domain name registries and DNS service providers. So the size test affects not only whether you are caught but which category you land in. Member states can also designate specific smaller entities, and public administration bodies are covered in many cases.
If your organization is in scope, one of the first practical steps is registration: in-scope entities submit their details to their national competent authority. For certain cross-border digital providers, that information also feeds an EU-level registry that ENISA maintains, but organizations register through their national authority rather than with ENISA directly. Working out your category early matters, because it decides whether you face proactive supervision or ex-post supervision that an authority can open whenever it sees indications of possible non-compliance.
The controls NIS2 requires are common across these sectors, but the specific risks are not. Organizations in energy contend with supply-chain exposure, ageing technology and tightly interconnected systems; those in transport with ransomware and limited security investment; and those in finance with phishing, web-based attacks and social engineering. Where the pressure falls is shaped by the industry you operate in.
Where Does NIS2 Enforcement Stand in 2026?
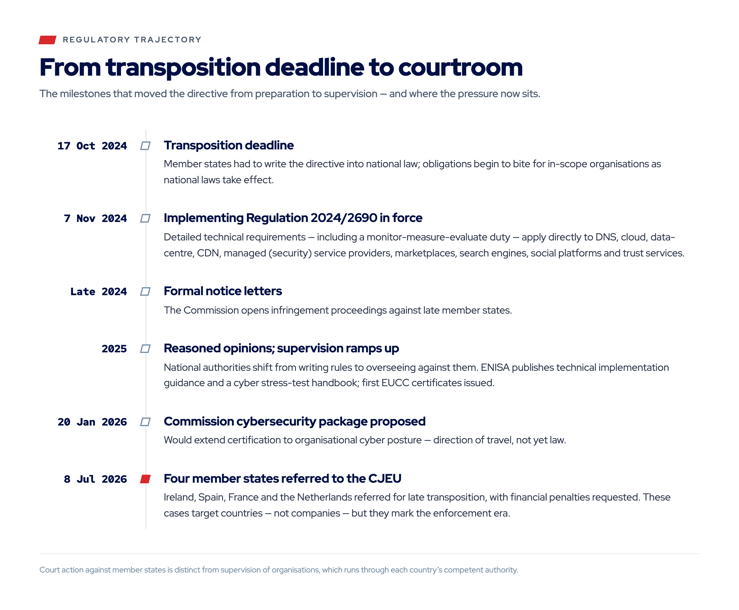
The deadline for member states to write NIS2 into national law was 17 October 2024. By mid-2026, most had done so, though several were late. The Commission pursued the laggards through the usual infringement steps: formal notice letters in late 2024, reasoned opinions in 2025, and then, on 8 July 2026, referral of Ireland, Spain, France, and the Netherlands to the Court of Justice of the EU, with a request for financial penalties that accrue until each completes transposition.
Court action against countries is not enforcement against companies. It is worth being precise here, because the two are easily confused. Those court cases are against member states for failing to transpose the directive on time; they are not prosecutions of organizations for non-compliance. For organizations, the more relevant shift is quieter: as national laws take effect, the competent authorities each country designates are moving from writing rules to supervising against them. How active that supervision is varies by country and is still developing.
Supervision, and its consequences, depend on your category and your country. Essential entities face proactive supervision, meaning authorities can audit and inspect them without waiting for an incident. Important entities are subject to ex-post supervision: an authority can act whenever it receives evidence, indications or information suggesting possible non-compliance, not only after a cybersecurity incident. The penalty ceilings are set by the directive, up to €10 million or 2% of total worldwide annual turnover for essential entities and up to €7 million or 1.4% for important entities, but the sanctions that actually apply, and how vigorously they are enforced, are set by each national transposition rather than uniform across the EU.
Management accountability is real, and partly EU-wide. Under Article 20, an organization's management body must approve its cybersecurity risk-management measures, oversee their implementation, and take cyber security training; these duties are consistent across the EU. Enforcement has an EU-wide backstop too: for essential entities, NIS2 requires member states to ensure that, as a last resort, authorities can seek a temporary ban on individuals at CEO or legal-representative level from exercising managerial functions (public administration entities are exempt from this particular measure). Beyond that, personal fines and other personal liability depend on national transposition. The durable point is that accountability now sits with leadership, not only with the security team.
NIS2 Cybersecurity Requirements
NIS2 sets a baseline that every in-scope organization must meet. The main obligations fall into a few groups.
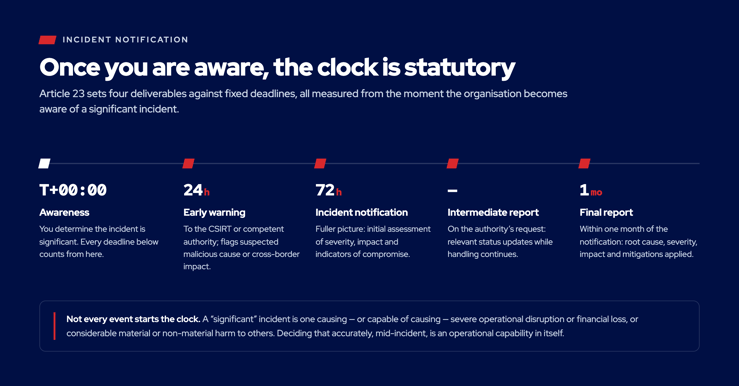
Risk-management measures (Article 21). Organizations must take appropriate and proportionate measures to manage cyber risk, and Article 21 lists ten as a minimum: risk analysis and information-system security policies; incident handling; business continuity and crisis management; supply chain security; security in acquisition, development, and maintenance, including vulnerability handling; basic cyber hygiene and training; cryptography and encryption; human resources security, access control, and asset management; multi-factor authentication and secure communications; and, crucially, policies and procedures to assess the effectiveness of those measures (Article 21(2)(f)). That last point is easy to overlook and central to everything that follows: NIS2 does not just ask whether a control exists, it requires you to have a way of testing whether it actually works.
Corporate accountability (Article 20). As above, management must approve, oversee, and stay trained on the organization's cyber risk. Responsibility reaches the top, not just the IT department.
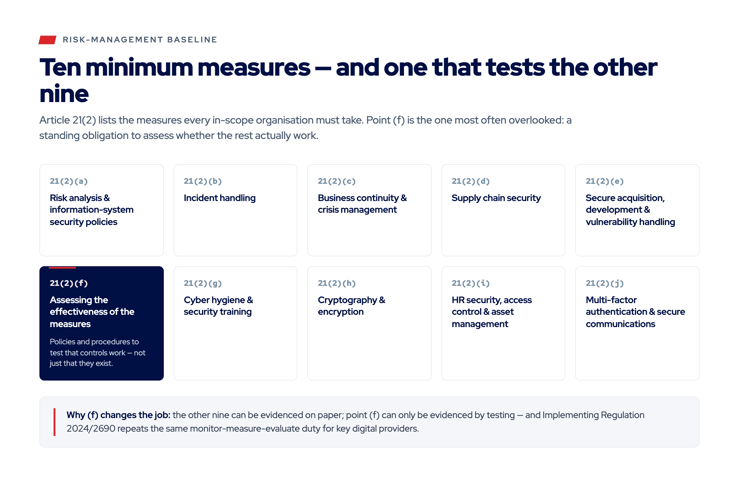
Incident reporting (Article 23). Significant incidents must be reported to the national CSIRT or competent authority on a strict timeline that starts when you become aware of the incident: an early warning within 24 hours, a fuller notification within 72 hours, an intermediate report if the authority asks for one, and a final report within one month of the notification. "Significant" has a specific meaning, an incident that causes or can cause severe operational disruption or financial loss, or considerable material or non-material harm to others, so not every detected event triggers the clock. Doing this accurately during a live incident is an operational capability, not a policy statement.
Business continuity. Organizations must be able to keep critical services running, or restore them quickly, when a serious incident hits, which means backups, recovery plans, crisis procedures, and a response team that knows its job.
One specific group has an extra layer of detail. Implementing Regulation (EU) 2024/2690, in force since 7 November 2024, sets out detailed technical and methodological requirements, and defines when an incident counts as significant, for a defined set of digital providers: DNS service providers, TLD name registries, cloud computing and data-centre providers, content-delivery networks, managed service providers, managed security service providers, online marketplaces, online search engines, social-networking platforms and trust service providers. It applies directly in every member state without national transposition. Notably, its annex requires these providers to monitor, measure, and evaluate the effectiveness of their security measures, reinforcing the same testing obligation found in Article 21(2)(f). ENISA published technical implementation guidance in 2025 to help organizations meet it.
Does NIS2 Require Certification? What "Certification" Really Means
This is the area where NIS2 is most often misunderstood, so it is worth being precise.
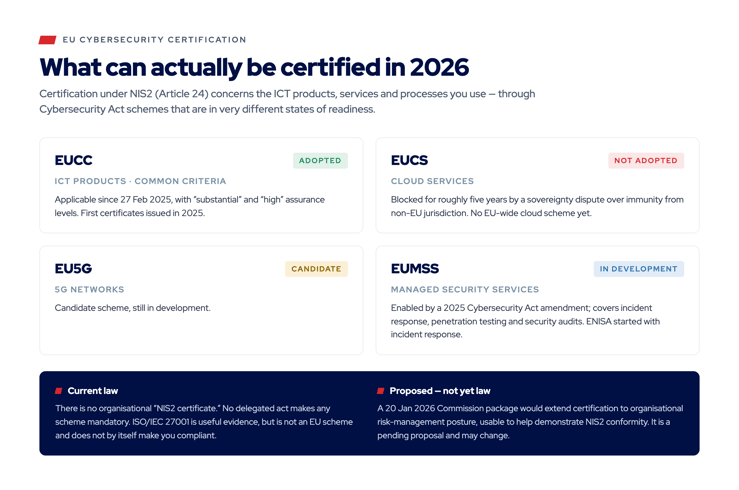
Under the rules currently in force, there is no EU-wide organizational "NIS2 certificate." NIS2 is a directive you comply with; you cannot, today, become "NIS2-certified" the way you can be certified against a standard like ISO/IEC 27001. Where NIS2 talks about certification, it concerns the security of the ICT products, services and processes you use, not a stamp of approval for your company. (A January 2026 proposal would change this; more on that below.)
The relevant provision is Article 24. It lets member states require essential and important entities to use ICT products, services, and processes, whether built in-house or bought from suppliers, that are certified under a European cybersecurity certification scheme created under the EU Cybersecurity Act (Regulation (EU) 2019/881). It also lets the European Commission adopt delegated acts to make specific certifications mandatory for defined categories of entities, but only where a cybersecurity gap has been identified, following an impact assessment, and with an implementation period. As of 2026, no such delegated act has been adopted, so there is currently no EU-wide mandatory certification requirement under NIS2. A separate provision, Article 25, encourages the use of European and international standards without forcing particular technologies.
The schemes themselves are still being built out under the Cybersecurity Act. Only one, the EUCC, is fully adopted: applicable since February 2025 and based on the international Common Criteria standard, it certifies ICT products at "substantial" and "high" assurance levels. Schemes for cloud services (EUCS), 5G and managed security services are still in development, so none of them yet creates a NIS2 obligation.
What about ISO/IEC 27001? It remains genuinely useful. It demonstrates a working information security management system, maps closely to several Article 21 measures, and auditors treat it as meaningful evidence. But it is not a European cybersecurity certification under NIS2, and holding it does not, by itself, make you compliant. The obligation on your organization is to meet the Article 21 measures and be able to demonstrate them; certification of the ICT products, services and processes you use is a complementary piece, and for now largely a voluntary one.
Everything above describes current law. On 20 January 2026, the European Commission published a cybersecurity package that includes a proposed revision of the Cybersecurity Act and targeted amendments to NIS2. Among other things, it would extend certification beyond individual products and services to an organization's overall risk-management practices and cyber posture, so that a certificate could be used to help demonstrate NIS2 conformity, with member states able to make such certification mandatory for some essential or important entities and voluntary for others. Treat this as direction of travel, not obligation: it is a proposal working through the EU legislative process, and the detail may change before it becomes law. As things stand, there is still no organizational NIS2 certification.
How to Achieve NIS2 Compliance: A Practical Checklist
Every organization's path differs, but the sequence is broadly the same:
1. Confirm scope and register with your national competent authority.
2. Put management in charge — Article 20 accountability, oversight and training.
3. Run a gap and risk assessment against the Article 21 measures.
4. Implement the ten Article 21 measures, from access control and encryption to supply-chain security.
5. Stand up incident reporting that can meet the Article 23 clock (24 hours, 72 hours, one month).
6. Build and exercise business continuity — backups, recovery and crisis plans.
7. Secure your supply chain and keep a third-party risk register.
8. Train your people and keep the records.
9. Test effectiveness and keep the evidence, continuously (Article 21(2)(f)) — the step most often underestimated, and where cyber-range testing does the most.
Operational Technology (OT) and NIS2: Testing What You Can't Take Offline
Much of what NIS2 protects does not run on ordinary IT. Energy grids, water and wastewater plants, transport systems, manufacturing lines and hospital equipment depend on operational technology (OT): the industrial control systems, SCADA, PLCs and sensors that run physical processes. Those are precisely the Annex I and II sectors NIS2 puts at its centre, so OT is squarely in scope, not a niche concern.
OT is also the hardest part of an estate to secure, and the hardest to test. It is built for availability and safety first, so systems cannot simply be patched or rebooted on demand; much of it is long-lived and predates modern security design; and as OT converges with IT for remote monitoring and data, the attack surface grows while the legacy equipment gets no easier to defend. The bind for NIS2 is direct: the Article 21 measures, incident handling, business continuity and the duty to assess effectiveness under Article 21(2)(f) all apply to OT, but you cannot launch an attack against a live grid or production line to find out whether your defences and your people hold. The risk to physical operations, and to safety, is too real.
OT assurance therefore leans on methods that keep the live process safe. Several are non-intrusive by design: passive network monitoring, configuration and architecture reviews, recovery tests during planned maintenance windows, and other carefully controlled assessments. But to see how OT behaves under a real attack, without endangering the process it controls, you generally have to work against a replica, and two layers matter most:
· Tabletop exercises bring engineering, operations, security and management to one table to walk through an OT incident, a compromised controller, or a ransomware event forcing a plant offline, and to rehearse the decisions where safety, continuity and the Article 23 reporting clock collide. In OT those cross-disciplinary calls are often the weakest link, and a discussion-based exercise is the safest way to expose them.
· Digital-twin cyber ranges go further, recreating the OT environment as a high-fidelity replica where real attacks can be run, detection and controls observed, and containment and recovery practised, without the risks that come with testing on live systems. It is one of the strongest ways to generate the effectiveness evidence NIS2 expects for OT, and it works alongside those other methods rather than replacing them.
CybExer's digital twin capability is built for exactly this: standing up a faithful model of an OT environment so that critical-infrastructure operators can test controls, teams and response under realistic attack without ever touching the systems that keep the lights on.
How These Recent Changes Tie to Cyber Range Testing
Step back and two threads run through everything above. First, NIS2 no longer accepts documentation as proof: Article 21(2)(f) and the Implementing Regulation both require organizations to assess whether their security measures actually work, and testing is the most convincing way to do that. Second, the wider direction of EU policy keeps moving toward tested, demonstrable security capability rather than documentation. Both threads point at the same thing: capability observed under realistic conditions, not claims on paper.
This is exactly what cyber range technology provides. A cyber range is a safe, instrumented environment where an organization can recreate its own systems, tools, and teams and put them through realistic cyber attacks with no risk to live operations. The EU is pointing the same way: in 2025, ENISA published a Handbook for Cyber Stress Tests, a structured method for assessing how well critical organizations would cope during and after a serious incident, in line with NIS2. The premise is the one NIS2 now enforces, that resilience is something you test for, not something you assume.
For an organization inside, or moving toward, NIS2 scope, a cyber range maps directly onto the obligations:
Assess the effectiveness of your measures (Article 21(2)(f)). This is the obligation that documentation cannot satisfy. Running your defenses against realistic, evolving attacks is how you find out whether the controls you have mapped actually hold, and it produces the evidence that you assessed them.
Rehearse the reporting clock (Article 23). Run realistic incidents against the actual 24-hour and 72-hour deadlines and see whether your detection, decision-making, and reporting genuinely fit inside them.
Exercise incident response and business continuity (Article 21(2)(b) and (c)). Move plans off paper and into practice, surface the gaps that only appear under pressure, and build the record of testing that auditors increasingly ask to see.
Train people and prepare management (Article 21(2)(g) and Article 20). Give technical teams realistic practice, and give boards and executives a setting to exercise the oversight and decisions that Article 20 makes their personal responsibility.
Produce audit-ready evidence. Every exercise creates a record: the actions taken, the attacks detected or missed, the time to detect and respond, and a full audit trail. That kind of instrumented evidence stands up to a supervisory review far better than an untested policy.
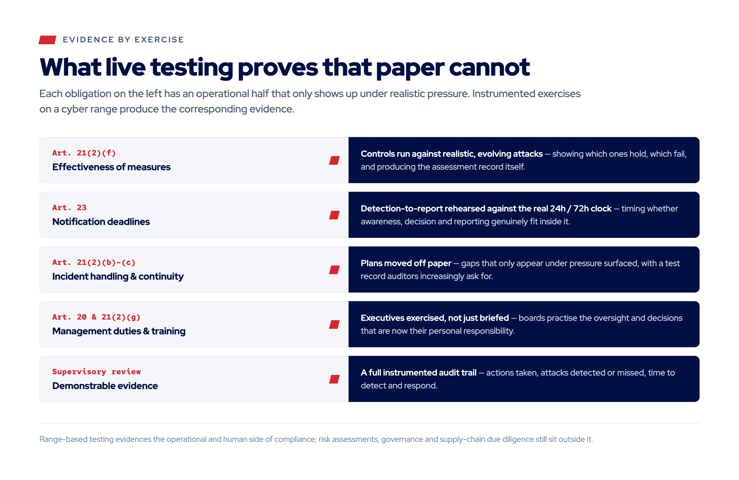
It helps the argument to be honest about the limits. A cyber range is not a whole compliance programme. It is strong evidence for the operational and human side of NIS2, whether your controls hold under attack, whether your team can run the reporting clock, whether your incident-response and continuity plans work in practice. It does not produce your risk assessments, governance and policy framework, or supply-chain due diligence, and it is not a certification. Range-based testing is one component of a broader NIS2 assurance programme; its value is that it evidences the parts documentation cannot.
CybExer provides cyber range and digital twin capabilities built for exactly that component. We recreate an organization's real operating environment so that its teams, processes, and technology can be tested against realistic cyber pressure, before an incident, or an auditor, puts them to the test. If demonstrating those operational and human capabilities is part of your NIS2 assurance plans, our cyber range experts can help you work out what an appropriate setup would look like for your sector.
Conclusion
NIS2 has entered its enforcement phase. It is now law across most of the EU, supervisory authorities are moving from rule-making to oversight, and accountability for cybersecurity reaches management, in forms each member state is still defining. The rules keep pointing in one direction: it is not enough to describe your defenses, you have to be able to demonstrate them, and the directive itself now requires you to assess their effectiveness.
Certification has a role, but a narrower one than the marketing around NIS2 often suggests: today it concerns the products and services you use rather than the organization itself, and proposals to extend it to organizational posture are still just proposals. It is no substitute for meeting and proving the directive's core obligations. That is where the real work sits, and it is where cyber range testing earns its place, as the part of a broader assurance programme that turns documented intent into demonstrated, evidenced capability. If you would like to talk about how this could work for your organization, get in touch with our team.
Frequently Asked Questions
Who needs to comply with NIS2?
Medium-sized and larger organizations in one of NIS2's 18 sectors, split between "high-criticality" sectors in Annex I and "other critical" sectors in Annex II. The size test broadly means 50+ staff, or turnover or a balance-sheet total above €10 million, calculated under the EU's SME definition (so linked and partner companies count). Large organizations in Annex I sectors are essential entities; medium-sized ones, and qualifying Annex II organizations, are important entities. Some providers, such as DNS providers, top-level domain registries and trust service providers, are in scope regardless of size.
What is the NIS2 compliance deadline?
Member states had to write NIS2 into national law by 17 October 2024, and the obligations now apply to in-scope organizations. Several countries transposed late, and in July 2026 the Commission referred four of them to the EU Court of Justice, but those cases are about the countries' delay, not enforcement against companies. For organizations, the practical point is that national supervision is now ramping up.
Is there an NIS2 certification?
Not under the rules currently in force. You cannot become "NIS2-certified" as an organization today. NIS2 is a directive you comply with. Where it mentions certification (Article 24), it refers to using ICT products, services and processes certified under EU cybersecurity schemes such as the EUCC, and none of that is mandatory under NIS2 today. A January 2026 Commission proposal would add organizational-level certification, but that is pending legislation, not yet law.
What are the penalties for non-compliance?
The directive sets ceilings of up to €10 million or 2% of total worldwide annual turnover for essential entities, and up to €7 million or 1.4% for important entities. Management can also face personal consequences. For essential entities, the directive itself requires authorities to be able to seek, as a last resort, a temporary ban on individuals at CEO or legal-representative level from managerial functions; national law governs how that power is applied. Other personal liability, such as personal fines, depends on each country's transposition.
How is NIS2 different from GDPR or DORA?
GDPR protects personal data; NIS2 protects the security and continuity of essential and important services. DORA sets similar resilience rules specifically for the financial sector and generally takes precedence there. An organization can fall under more than one of these regimes at once.